Start with Ubuntu or a Debian-based virtual machine for daily practice, then bring in Kali Linux as a live image or dedicated VM once you’re ready to run penetration testing tools. This combination gives beginners a stable environment for learning core Linux skills while keeping specialized, higher-risk tools isolated. The rest of this guide breaks down distro choices, essential commands, security tools, and a phased path to get there.
TL;DR:
- Beginners should start with Ubuntu or Debian for daily tasks, reserving Kali Linux for specialized penetration testing in a separate environment.
- Building core Linux skills in command line, permissions, process management, networking, and Bash scripting is essential before tackling offensive tools.
- Learning fundamental security tools like Nmap, Wireshark, rkhunter, and hardening utilities provides a strong practical foundation for cybersecurity practices.
- Creating a contained practice lab using local VMs, WSL, or live USBs is crucial for safe experimentation and avoiding scope violations.
- A structured six-month learning plan should progress from command line mastery to networking, scripting, and supervised labs, with certifications like Security+ supporting career growth.
Table of Contents
- Which Linux Distro Should You Use for Cybersecurity?
- What Linux Skills Do Cybersecurity Beginners Need?
- Which Linux Security Tools Should You Learn First?
- How Do You Build a Safe Linux Practice Lab?
- What’s a Realistic 6-Month Learning Path?
- Where Instructor-Led Labs Fit Into Self-Study
- What Beginners Get Wrong About Learning Linux for Security
- Ready to Turn Practice Into a Credential?
- Sources
- FAQ
Which Linux Distro Should You Use for Cybersecurity?
The right distro depends on what you’re doing that day, not personal preference. Most learners run into trouble by installing Kali as their only operating system and then wondering why basic tasks feel harder than they should.
- Ubuntu or Debian: your daily driver. Stable, well-documented, and backed by the largest package ecosystem in the Linux world. This is where you build muscle memory for the command line, permissions, and networking before touching offensive tools.
- Kali Linux: a Debian-based distribution maintained by Offensive Security and built specifically for penetration testing and digital forensics. Run it as a live image or a VM, not as your primary system, since it ships with tools that can trigger antivirus alerts and network security policies when used carelessly.
- Fedora Security Lab: a live test environment with a customized security-testing menu, ideal for auditing and forensics practice without committing to a full install.
- Arch or BlackArch: worth exploring only after you’re comfortable troubleshooting your own system. These reward experience and punish shortcuts.
For setup mapping, treat Ubuntu as your VM or WSL environment for scripting and networking practice, and reserve Kali or Fedora Security Lab for a Live USB or a separate VM dedicated to tool work.
Pro Tip: Snapshot your VM before installing any new tool. Reverting a bad install takes ten seconds; rebuilding a broken environment from scratch can eat an entire evening.
What Linux Skills Do Cybersecurity Beginners Need?
CompTIA identifies five core Linux skill areas cybersecurity professionals should master: system and network administration, regular expressions, SELinux and AppArmor, open-source security tools, and Bash scripting. Build toward that list in this order:
- Command line fluency: navigation, piping, redirection, and text processing with
grep,sed, andawk. This is the skill that makes every other skill faster. - Permissions and user management:
chmod,chown,sudo, and how/etc/passwdand/etc/shadowdefine who can do what. - Process and service inspection:
ps,systemctl,journalctl, andtoporhtopto see what’s actually running on a system. - Networking commands:
ip,ss,netstat, and basictcpdumpusage to understand what a machine is talking to. - Bash scripting: automating repetitive checks so your workflows are reproducible instead of ad hoc.
- Basic hardening:
ufworfirewalldfor firewall rules,fail2banfor brute-force protection, and disciplined use ofaptordnfupdates.
None of this is exotic. It’s the same toolkit sysadmins have relied on for decades, applied with a security lens.
Pro Tip: Keep a running log of every command you learn, with a one-line note on what it’s for. Six months in, that log becomes your own reference manual, and it’s more useful than any cheat sheet you’ll find online.
Which Linux Security Tools Should You Learn First?
A handful of tools cover most of what a beginner needs to practice recon, packet analysis, and system integrity checking. Learn what each one does before worrying about advanced flags or automation.
- Nmap: the standard for network discovery and port scanning. Nmap is free, well-documented, and the right place to start practicing safe scanning, always against machines you own or a lab network you control.
- Wireshark and tcpdump: capture and inspect network traffic. Wireshark’s graphical interface makes packet structure easier to see for beginners, while tcpdump is the command line tool you’ll actually use on remote servers.
- rkhunter: a rootkit hunter that checks system binaries and configuration against known-good baselines. Run it periodically on a lab machine to get a feel for what a clean integrity scan looks like versus a flagged one.
- Hardening tools like linux-hardener or HARDN: projects such as HARDN let learners scan a system, generate a compliance-style report, and preview changes before applying them, with rollback built in. That dry-run and revert pattern is a safer way to learn hardening than running scripts blind.
- OWASP’s Web Security Testing Guide: once you’re ready to test web applications, OWASP’s guide walks through methodology instead of just listing tools.
How Do You Build a Safe Linux Practice Lab?
Every exercise above needs a contained environment where mistakes cost nothing. You have four realistic options, and most learners end up using two of them together.
- Local VM: VirtualBox or VMware running Ubuntu and Kali side by side. Full control, works offline, and snapshots make experimentation low-risk.
- WSL: useful for Windows users who want Linux command line practice without a full VM, though it’s not ideal for network-level tool work.
- Live USB: boot Fedora Security Lab or Kali directly from a USB drive with no install. Fedora Media Writer makes this straightforward and leaves your host system untouched.
- Cloud ephemeral labs: browser-based sandboxes for when you need zero local setup, good for quick practice sessions.
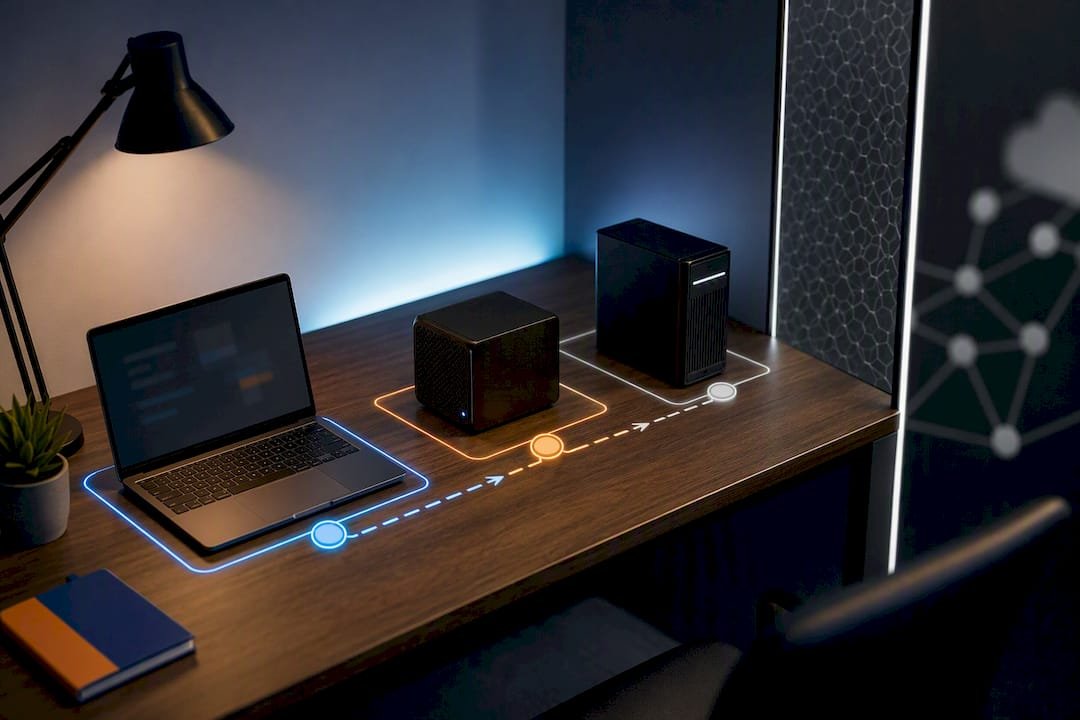
Keep your lab isolated with host-only networking, take a snapshot before any major change, and know how to revert instantly. A minimal setup that covers most needs: one Ubuntu VM for daily work, one Kali live image or VM for tool practice, snapshotted before you touch anything new.
Pro Tip: Never point a scanning tool at an IP address you don’t own or don’t have explicit written permission to test. Scope discipline isn’t optional, it’s the line between practicing and breaking the law.
What’s a Realistic 6-Month Learning Path?
Structured, phased learning, moving from command line to networking to scripting to labs, tends to align with both certification tracks and what employers actually expect on day one.
- Weeks 0 to 8: command line fundamentals, file permissions, and small scripting projects. Document every exercise as you go.
- Weeks 8 to 16: networking tools, packet analysis with Wireshark and tcpdump, Bash automation, and CTF-style challenges to apply what you’ve learned under light pressure.
- Months 4 to 6: supervised pentesting labs, incident response basics, and a portfolio project that shows a scan, a finding, and a remediation step, not just a screenshot of a tool running.
- Certifications: CompTIA Security+ is the common starting credential, followed by role-focused training once you know whether you’re leaning toward defense, offense, or operations.
Track this path against a structured prerequisites checklist and start building a portfolio of practical experience as early as Phase 1, not after you feel “ready.”
Where Instructor-Led Labs Fit Into Self-Study
Self-study covers the fundamentals, but supervised labs add feedback loops that solo learners rarely get on their own: scenario-based grading, a mentor who catches bad habits early, and structured exercises instead of scattered YouTube tutorials.
- Veterans and career changers often benefit most from guided programs because structure replaces guesswork.
- When evaluating any training program, check for actual lab access, real mentor availability, and direct alignment with certification objectives, not just a syllabus that name-drops exam codes.
What Beginners Get Wrong About Learning Linux for Security
Too many beginners chase the newest tool instead of drilling fundamentals that make every tool easier to learn later. Document every lab session, respect scope boundaries religiously, and repeat small projects until they’re automatic. One well-documented home lab beats a dozen half-finished tutorials.
— Alden
Ready to Turn Practice Into a Credential?
Reading about Nmap scans and Bash scripts only gets you so far. Some training programs build supervised lab time and mentor feedback into the training itself, so learners are not guessing whether their home lab habits match what employers actually test for.
Total Cyber Academy’s programs map directly onto the phases in this guide. The Penetration Tester Program picks up where Phase 3 leaves off, with supervised offensive labs instead of solo CTF practice, and the full course catalog covers everything from CompTIA Security+ through EC-Council’s CEH for learners ready to formalize their command line and networking skills into a certification. Every course pairs hands-on labs with live mentorship from working cybersecurity professionals, built specifically for veterans, career changers, and beginners who want structure instead of another abandoned tutorial series. Browse the program tracks that match where you are in your 6-month plan, and reach out to admissions for a straightforward next step.
Sources
- 5 Linux Skills You Must Master to Be a Cybersecurity Professional
- Kali Linux downloads
- Fedora Security Lab
- OWASP Web Security Testing Guide
FAQ
Which Linux Distro Is Best for Cybersecurity?
Ubuntu or a Debian-based distro is best for daily learning because of its stability and package support, while Kali Linux is the standard once you’re ready to practice pentesting. Kali is maintained by Offensive Security specifically for that purpose, and it works best run as a VM or live image rather than a daily operating system.
Is Linux Actually Used in Cybersecurity Jobs?
Yes. Linux underpins most servers, security appliances, and penetration testing toolkits, which is why CompTIA lists Linux administration and scripting among the core skills for cybersecurity roles. Command line fluency, permissions management, and Bash scripting show up constantly in day-to-day security work, not just in specialized tool use.
Can You Really Earn $200,000 a Year in Cybersecurity?
Senior and specialized cybersecurity roles, such as penetration testing leads or security architects, can reach that range, but it typically takes years of experience, strong certifications, and a track record of hands-on work to get there. Early-career salaries start well below that figure, which is why building a documented skills portfolio matters from your first lab session onward.
What Linux Distro Do Most Ethical Hackers Use?
Kali Linux is the most widely used distribution among penetration testers and ethical hackers because it bundles hundreds of security tools into one image. Most professionals still run a separate stable system, often Ubuntu or Debian, for daily work and reserve Kali for dedicated testing tasks.
Do I Need a Certification to Start Learning Linux for Cybersecurity?
No certification is required to start, since free distros, documentation, and lab environments are enough to begin building skills today. A structured path like Total Cyber Academy’s beginner certification plan helps once you’re ready to formalize those skills for employers.